Cybersecurity
IT System Security: A Practical Guide for Business
A practical approach to securing business IT systems: risk management, MFA, endpoint protection, segmentation, backup, monitoring and incident response.
Read articleExplore our articles
Protecting data, people and operations. Preparation before an incident.
A practical approach to securing business IT systems: risk management, MFA, endpoint protection, segmentation, backup, monitoring and incident response.
Read articleHow antivirus software works, when built-in protection may be enough, and what businesses need from endpoint security, EDR and managed monitoring.
Read article
Security procedures often fail for a simple reason: they are written as documents, not as a way of working. The company gets a policy, a folder, a few general statements and the impression that something has been completed.
Read article
The NIS2 directive is a European framework that raised expectations for organizations that depend on digital systems. For companies outside the EU, including Serbian companies that work with EU partners, it matters because it shows where modern cyber risk management is moving: cybersecurity is no…
Read article
An information system security policy is not just a document created to satisfy a formal requirement. Its real value is to define how a company protects its systems, data, users, employees and business continuity.
Read article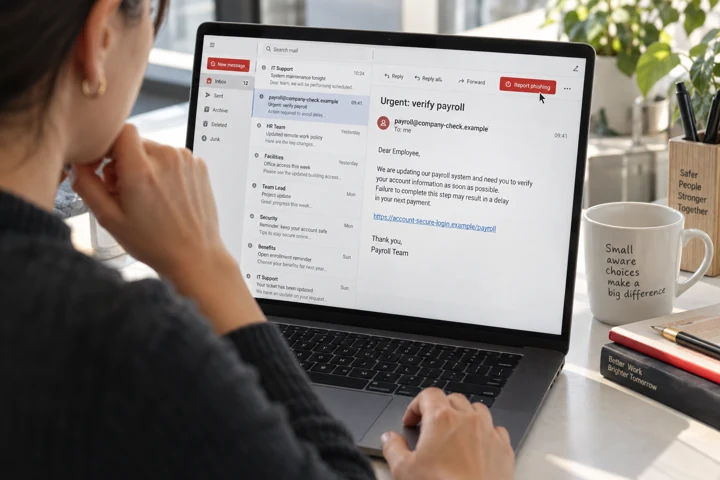
In cybersecurity conversations, employees are often described as the biggest risk. That is a shallow and dangerous simplification. People can make mistakes, but they can also become the fastest sensor for a problem.
Read article