In this article17 sections
Protecting a company from cyber threats is not merely an IT department task or a matter of installing antivirus software. Ransomware, phishing, service outages and data loss can interrupt everyday work and undermine customer trust. Positive's original “Zaštitite svoj biznis” article treated cybersecurity as part of business stability and organised its advice around five connected areas: understanding threats, implementing basic controls, training employees, using advanced security tools and preparing an incident response plan.
Editorial note (October 2026): This is a faithfully restored and substantially expanded edition of Positive's “Zaštitite svoj biznis”, originally published on 31 January 2025 by Positive in the Cybersecurity category. The original ransomware, phishing and DDoS examples, business consequences and all five thematic areas are retained. The 2026 additions discuss stronger authentication, tested backups, structured risk management, NIST CSF 2.0 and business continuity. These are not records of a completed Positive client project, measured customer outcomes or a promise of complete protection.
Cybersecurity: Protect your business against modern threats
In a digital business, people access important information from computers, mobile devices, various networks and cloud services. More access points create valuable ways to work, but also increase the need to govern identities, devices, applications and information. An attack does not need to affect every system to cause serious disruption. Loss of email, customer records, billing services or shared operational documents can stop multiple teams from completing their responsibilities.
Cybersecurity therefore cannot be assessed solely by how many malicious files an antivirus application has blocked. Organisations need to understand which threats matter, how quickly incidents can be noticed, who responds and whether essential services can be restored safely. The aim is to reduce both likelihood and impact, not to claim that technology eliminates uncertainty or guarantees that attackers will never succeed.
Original pillar one: Understanding cyber threats
The original Positive article advised companies to recognise common attacks and understand their consequences before selecting tools. It highlighted three categories: ransomware, phishing and Distributed Denial of Service (DDoS). A contemporary review should also consider compromised legitimate accounts, poorly protected remote access, unpatched software and dependencies on external providers. The significance of each threat varies with the sector, working methods, data and systems on which an organisation relies.
A useful starting point is to list the services that would halt operations if unavailable, identify where sensitive information is stored and determine who has administrator privileges. The best-known attack type is not automatically a company's greatest risk. Priorities should follow real exposure, the business consequences of disruption and the organisation's capacity to respond or recover.
Ransomware: Encryption, disruption and possible data theft
Ransomware may encrypt business files or interrupt services, and some attacks also involve stealing information before attempting extortion. For a company, the consequences extend beyond technical damage: orders, billing, communication and production may stop while teams investigate. Paying a ransom, even if considered, offers no guarantee of safe or complete data restoration.
Risk reduction therefore involves identity controls, sensible separation of access, software maintenance and backups that attackers cannot easily modify or destroy. CISA recommends keeping protected, offline or suitably isolated backup copies and testing recovery procedures. A file labelled “backup” is not evidence that a business can restore operations. A verified restoration process with clear priorities is far more useful than an untested assumption.
Phishing: Messages that exploit people and identity
Phishing relies on deceptive messages and websites designed to persuade people to disclose credentials, approve access, run malicious content or transfer money incorrectly. It may resemble an urgent instruction from management, a supplier's new bank details or a Microsoft 365 sign-in alert. Familiar branding and a professional tone are not proof that a message is legitimate, and a genuine contact's account may have been compromised.
Good protection combines technical controls and habits: multifactor authentication, independent verification of unusual financial instructions and a straightforward route for reporting suspicious messages. Telling employees simply to “be careful” is insufficient. They need concrete examples, a clear escalation procedure and an understanding of what to do if they click or disclose something by mistake.
DDoS: When a public-facing service becomes unavailable
A Distributed Denial of Service attack attempts to overload an accessible service through large volumes of traffic or requests. A website, customer portal or important online channel may become difficult or impossible to reach. For companies that sell or support customers online, that can mean lost inquiries, interrupted service and damaged trust. A DDoS attack is not inherently identical to data theft, even though multiple kinds of attack can occur together.
Resilience may depend on network and infrastructure-provider protections, service-availability monitoring, agreed contacts and alternative communication plans. Organisations should know who controls domains, hosting, DNS and defensive settings. Even technically effective protection loses value when the appropriate responsible person cannot authorise a response or reach the provider at the moment of disruption.
Business consequences: Information, finances and reputation
Positive's original text identified three important consequences: loss of confidential data, financial losses and damage to reputation. These often reinforce one another. An outage can delay delivery, create recovery expenses and undermine confidence among customers and partners. If personal or contractual information is exposed, an organisation may also need to examine notification duties and other requirements arising from applicable law, contracts and its own documented procedures.
Instead of discussing consequences only in general terms, determine how long each critical process can be unavailable, which information must be restored and who needs to be notified. This business impact perspective helps managers prioritise security investments according to the operations at risk, not simply according to the visibility or price of a particular technology.
Original pillar two: Implementing basic security measures
Fundamental security controls create the foundation. The original article specifically mentioned antivirus and firewall protection, regular updates, strong passwords and two-factor authentication. Modern workplace security additionally needs controlled identities, suitable endpoint protection, restriction of administrator privileges and scrutiny of services exposed to the internet. None of these measures is a stand-alone guarantee of a secure organisation.
The immediate objective is to remove common and avoidable weaknesses. Business-critical applications and devices should have named owners, a patching process and expected security settings. New employees should receive access appropriate to their roles; departures should trigger timely account and access removal. Consistent foundations make more advanced technologies useful instead of leaving serious gaps hidden beneath sophisticated dashboards.
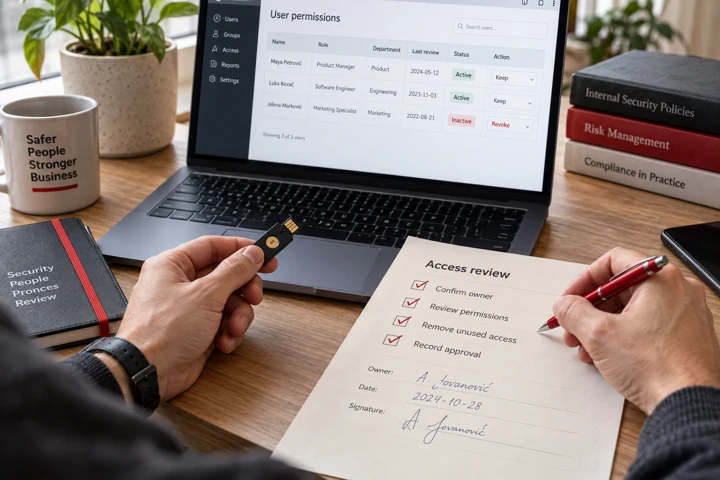
Passwords, MFA and management of user permissions
A strong password matters, but it is not sufficient when reused across services or given to a convincing impostor. Organisations benefit from unique credentials, password managers where appropriate, multifactor authentication and limits on unnecessary privileges. Email, remote access, privileged accounts and cloud administration deserve special attention because one compromised identity can affect many interconnected systems.
Where supported and suitable, consider phishing-resistant MFA. Review administrative accounts, shared identities and exceptions to normal access rules. High-risk business changes, such as altered supplier payment instructions, should also require independent confirmation through a trusted channel. Identity security is a combination of technology, operational discipline and clearly assigned responsibility rather than a one-time password policy.
Updates, endpoint security, firewalls and device health
Software updates address known vulnerabilities, while endpoint protection and firewalls may help prevent or detect various malicious activities. Still, having a product installed does not prove it is configured correctly, receiving updates or being monitored. Unsupported devices, unnecessary internet-facing services and obsolete accounts can remain major risks even when antivirus software is present.
A reasonable routine involves a hardware and software inventory, scheduled patches, a procedure for urgent security fixes and timely review of relevant alerts. Changes should be implemented carefully, with attention to potential impact on business applications. Companies need to know who supports workstations, servers, networks and software, and who verifies that an important protective action was completed rather than merely requested.
Original pillar three: Training employees
The original Positive guide presented employee education as a vital security measure. The aim should not be to blame people as the “weakest link”, but to equip them to recognise deception, use business devices responsibly and report unusual events quickly. Training topics include phishing emails, suspicious attachments, password sharing, remote work, unknown storage devices and procedures to follow when something goes wrong.
Short, repeated exercises connected to daily working situations may be more useful than one generic annual lecture. Employees should know exactly who receives an incident report and should be able to report a mistake without fear of immediate blame. Prompt reporting gives technical teams an opportunity to contain an incident even after an employee has clicked a link or exposed information.
Original pillar four: Advanced security tools and systems
For more complex or sensitive environments, the original article mentioned intrusion detection and prevention systems (IDS/IPS), encryption and security-log analysis. Intrusion monitoring may reveal unusual network activity; logs can support investigation of events; appropriate detection processes can highlight suspicious behaviour earlier. These measures are useful only when they are correctly configured, generate meaningful information and connect to people capable of responding.
Advanced technology does not replace foundational controls. If nobody reviews an alert, privileged access is excessive or incident contacts are undefined, an additional dashboard may simply add more unprocessed data. Security investment should follow actual business risks, infrastructure complexity, protection needs and the organisation's capacity for continuous management.
Encryption, logging and protection of confidential information
Encrypting information in storage and during transfer can reduce the impact of certain kinds of unauthorised access, provided encryption keys are managed responsibly. Access controls determine who is permitted to view, modify or export documents. Security logs can help reconstruct who accessed systems, what occurred and how the response unfolded. Organisations should not collect and retain unlimited information merely because the technology makes that possible.
A more mature company identifies sensitive information, assigns system owners and defines retention and deletion rules. Duties toward customers and regulators depend on specific applicable legislation and contracts. Deploying encryption or intrusion detection is not, by itself, proof of compliance. Evidence of an operating process matters more than a list of purchased features.
Backups and recovery: Restoration needs to be tested
Although the original guide focused more heavily on preventing attacks, reliable recovery is central to keeping a business operating after an incident. Backups should reflect the importance of the information being protected, resist unauthorised changes and be verified by real restoration tests. Ransomware scenarios especially require copies separated from the production environment or otherwise protected against an intruder's ability to delete and encrypt them.
A copy of business files is not the same as a plan to restore the full workflow. Companies must identify which applications return first, how much recent information they could afford to lose and how long essential services may remain unavailable. Concepts such as recovery point objective (RPO) and recovery time objective (RTO) can clarify expectations, but they need to match actual capability. Recovery that has never been practised is an assumption, not an established result.
Original pillar five: Planning an incident response
The original article closed with an incident response plan covering incident identification, damage assessment, notification of relevant parties and restoration of operations. Improvisation becomes costly when a suspicious event is underway. A workable plan defines who assesses the situation, who authorises isolation, who preserves evidence and who communicates with staff, customers, providers and authorities when required.
The first priority is to limit further harm safely while preserving relevant information for investigation. Analysis, controlled restoration and lessons learned should follow. Run regular exercises, including a scenario in which normal email and contact systems are unavailable. Quick restoration and secure restoration are not identical: systems suspected of compromise should not simply be returned to production without suitable investigation and checks.
Modern context: NIST CSF 2.0 and leadership responsibility
The NIST Cybersecurity Framework 2.0 describes six functions: Govern, Identify, Protect, Detect, Respond and Recover. These are not literally the same classification as Positive's original five topics, but they share an emphasis on understanding risk, preventing harm, detecting problems and preparing to respond. The additional Govern function makes leadership responsibility particularly clear: policy, risk priorities and accountability cannot exist solely inside the IT department.
Management should understand which services are critical, who can make decisions during an incident and which recovery scenarios have been prepared. The framework does not require every smaller organisation to implement identical controls mechanically. A sensible programme assesses the current position, desired outcomes and feasible next steps in proportion to business complexity and exposure.
Where to begin: Priorities, owners and measurable improvements
Start with the business processes and services that could be seriously disrupted. Then review access controls, MFA, patching, endpoint protection, backup arrangements and the ability to detect suspicious activity. Every important weakness should have an owner, realistic deadline and a way to verify that the protective change was actually implemented. A concise set of closed risks is more valuable than an extensive assessment that leaves responsibilities unclear.
The next step is a practical exercise: restore representative data from backup, practise reporting a phishing attempt or walk through a realistic incident scenario. Record how long it takes and what prevents an effective response. Only then decide which additional technologies or support arrangements are justified. Cybersecurity is a continual management process, not a project that can be declared permanently finished.
CoreTech and conclusion: Business continuity, security and trust
Within the current Positive ecosystem, CoreTech covers IT infrastructure, cybersecurity, support and backup services. Relevant directions include IT strategy, IT Care, Cyber Security and Backup & Recovery. These areas can help organisations assess their existing environment and develop a better managed foundation. Specific packages, delivery conditions, response commitments and capabilities require an assessment; no service makes cyber incidents impossible.
The source article's central message remains relevant: protecting a business means protecting data, continuity and customer confidence, not only computers. A company that understands threats, maintains basic safeguards, trains staff, monitors its environment and exercises recovery has a stronger basis for resilience. Learn more about the CoreTech ecosystem or contact Positive to discuss next steps.
Frequently asked questions
How should a business start improving cybersecurity?
Identify critical processes and data, verify MFA, software updates, endpoint protection and backups, then assign owners and establish a response plan.
Which threats did the original Positive article describe?
Ransomware, phishing and DDoS, alongside consequences such as data loss, financial harm and reputational damage.
Do antivirus software and firewalls guarantee security?
No. They contribute to baseline defence alongside patching, MFA, access controls, training, monitoring and recovery planning.
What role do employees play in cybersecurity?
They need to recognise phishing and suspicious behaviour, use devices safely and report concerns promptly through a clear process.
What should cyber incident response include?
Identification and containment, impact assessment, evidence preservation, required notifications, safe recovery and lessons learned.
Why must backups be tested?
Because having copies does not establish that data and critical services can be safely restored within the required timeframe.