Cybersecurity
IT System Security: A Practical Guide for Business
A practical approach to securing business IT systems: risk management, MFA, endpoint protection, segmentation, backup, monitoring and incident response.
Read articleExplore our articles
Protecting data, people and operations. Preparation before an incident.
A practical approach to securing business IT systems: risk management, MFA, endpoint protection, segmentation, backup, monitoring and incident response.
Read articleHow antivirus software works, when built-in protection may be enough, and what businesses need from endpoint security, EDR and managed monitoring.
Read article
The NIS2 directive is a European framework that raised expectations for organizations that depend on digital systems. For companies outside the EU, including Serbian companies that work with EU partners, it matters because it shows where modern cyber risk management is moving: cybersecurity is no…
Read article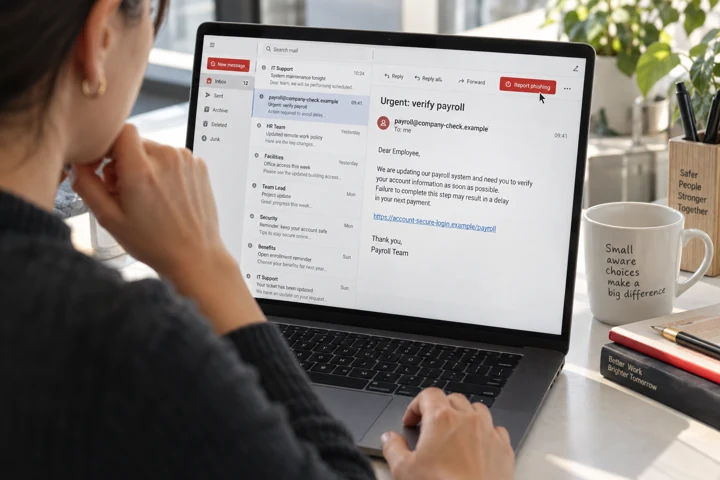
In cybersecurity conversations, employees are often described as the biggest risk. That is a shallow and dangerous simplification. People can make mistakes, but they can also become the fastest sensor for a problem.
Read article
Companies rarely ignore security because they believe it does not matter. More often, they believe it is already sufficiently covered. They have antivirus software. Someone maintains the computers. Passwords exist. Backup exists.
Read article
Cybersecurity is still often treated as a technical task that belongs only to the IT department. That view is understandable, but it is no longer enough.
Read article