In this article13 sections
AI agents change business because AI no longer has to stop at producing an answer. When connected to appropriate tools, data and rules, an agent can receive a goal, decide what to do next, use permitted systems, inspect the result and continue until the task is complete or a human checkpoint is reached.
That does not mean an organization should automate every decision. The more an agent is allowed to do, the more important permissions, boundaries, monitoring and human accountability become.
What is an AI agent?
An AI agent is a software system in which a model can do more than generate text. It can use defined tools and work through a sequence of steps toward a goal.
A simple AI assistant may read a document and answer a question. An agent can read a request, retrieve relevant information, check status in another system, call a permitted function, inspect the result and decide whether another step is needed.
In practice, an agent combines instructions, a model, tools, approved sources or context, validation rules and a way to escalate to a person.
An AI agent is therefore not “AI that can do everything on its own.” A useful business agent operates inside a deliberately limited scope.
Chatbot, assistant, automation or agent?
A chatbot is usually a conversational interface. It receives a question and returns an answer, sometimes grounded in a knowledge base.
An AI assistant helps a person with a defined job: finding information, preparing content, analysing a document or suggesting a next step. The person usually remains responsible for executing the action.
Traditional automation follows a predetermined flow. If A happens, the system performs B and then C. It is excellent when rules are stable and exceptions are limited.
An AI agent becomes useful when the sequence is not always identical. It can choose the next permitted action based on what happened in the previous step.
This distinction matters. A stable workflow should often remain ordinary software or rule-based automation. An agent is justified when the work requires adaptation, tool selection or reasoning across changing information.
What an agent looks like in a real workflow
Imagine a customer request: “My order has not arrived, I am travelling tomorrow and the delivery address may be wrong.”
A normal chatbot can explain the general policy. An agent, if permitted, can locate the order, check delivery status, determine whether the address can still be changed, read the exception policy and prepare options for the customer. If the case creates financial or operational risk, it can escalate to an employee with the context already assembled.
The same pattern works internally. An agent can receive an employee request, check documentation and system status, prepare a response, create a task and wait for approval before an action that changes business data.
The value is not that an agent “thinks like a person.” The value is that it can connect information and steps that previously required manual switching between systems.
Where AI agents can create value
In sales, an agent can prepare an account brief before a meeting, enrich CRM records with approved information, draft follow-up and create the next task.
In customer support, it can classify a request, consult the knowledge base, retrieve relevant status and prepare or send answers only for approved scenarios.
In administration, it can collect data from several sources, prepare a document, check whether required fields are missing and route the request to the right owner.
In IT support, it can gather diagnostic information, match an incident to a known solution, create a ticket and perform low-risk routine steps, while higher-risk changes remain behind human approval.
For management, an agent can prepare decision context. Decisions that carry legal, financial, security or strategic accountability should not become autonomous simply because the technology makes it possible.
When an AI agent is the wrong answer
An agent adds unnecessary complexity when the work has stable rules and the same sequence every time. Ordinary automation may then be cheaper, more predictable and easier to test.
An agent is also a poor starting point when the organization does not have reliable information sources. If nobody knows which document is current, who owns the information or which version should be trusted, an agent only moves the existing chaos faster.
A third warning sign is unclear ownership. An agent cannot solve organizational ambiguity. If nobody owns the process, quality standard or response to failure, automating execution increases risk.
Before building an agent, ask the same question that should start any transformation initiative: what operating problem are we solving and what must be in place for the solution to be safe and measurable?
How to implement AI agents in a company
Start with one sufficiently clear use case.
First describe the current state. How many steps does the task require today? Which systems are used? Where does waiting occur? What information is copied manually? Which steps require judgment and which are routine?
Then define the outcome. Examples include reducing preparation time, shortening customer response time, reducing manual entry or increasing the share of requests completed without unnecessary handoffs.
The third step is to define sources and tools. The agent should receive only the capabilities required for the specific job. Reading a status and changing a status are different risk levels. Searching documentation and approving a financial transaction are not the same permission.
The fourth step is to define human checkpoints. Decide in advance which actions the agent may perform automatically, which actions it may only propose and which decisions always remain human.
The fifth step is testing against real scenarios. Ideal demonstrations are not enough. Tests need normal cases, exceptions, incomplete information, contradictory inputs and situations in which the correct behavior is to stop.
Permissions matter more than apparent intelligence
An agent connected to several business systems becomes a new kind of user of those systems.
That means identity, permissions and activity records have to be designed deliberately. An agent should not receive broad access simply because broad access is technically convenient.
Least privilege is a practical starting point. If an agent only needs to read information, it should not have write access. If it may update one status, it should not have general administrative rights.
It is equally important to record which tools were used, what was changed and where human approval occurred. Without that trace, investigating failures and improving the system becomes difficult.
Guardrails, approvals and human control
A good agent is not a system without brakes.
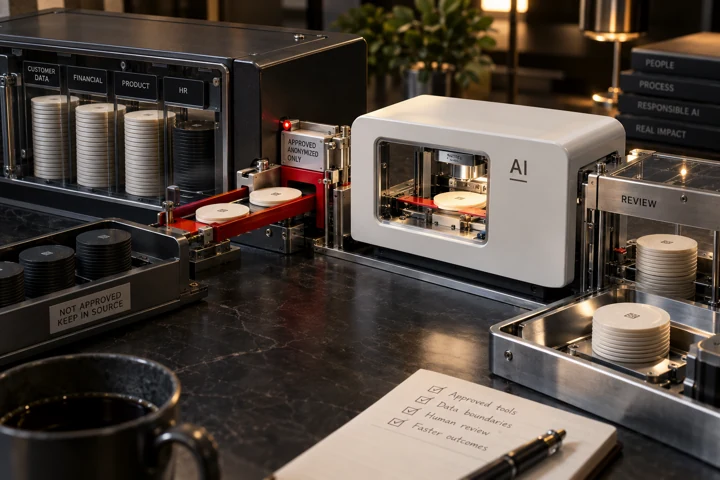
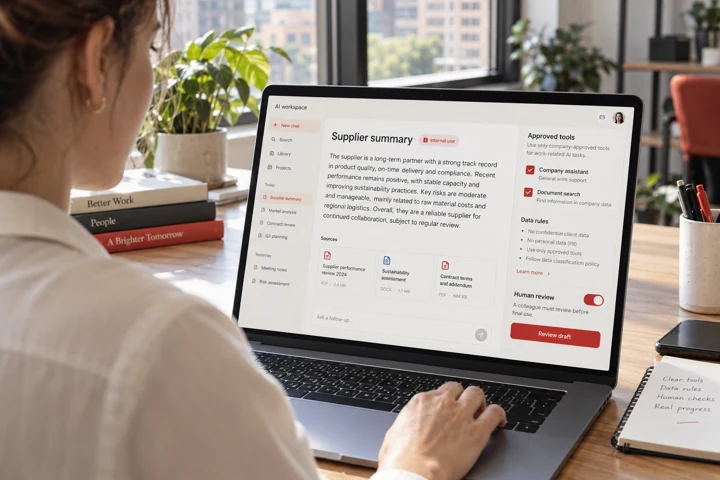
Guardrails can validate inputs and outputs, restrict categories of requests or stop execution when a result fails a defined check. Tools can be designed to expose only specific operations. Higher-impact actions can require explicit human approval.
It helps to think in three categories.
Low-risk actions may be automatic, such as searching approved documentation or preparing an internal summary.
A second category can be prepared by the agent but approved by a person, such as sending an important customer response, changing contractual information or creating an order.
A third category should remain human, particularly decisions that carry legal, financial, security or strategic accountability.
One agent or several specialist agents?
Not every problem is a multi-agent problem.
A single agent with well-defined tools is often easier to manage and test. Multiple agents are useful when there are clearly separated specialisms or when an orchestrator should delegate work to specialist roles.
A customer request, for example, may be handled by a main agent while specialist agents check billing, logistics or technical documentation. Another pattern is a handoff, where a specialist takes over one part of the workflow.
More architecture is not automatically better. Every additional agent creates more relationships that need to be tested, monitored and understood.
How to measure whether an AI agent works
Success is not the number of agent steps executed.
Measure the business outcome: cycle time, manual handoffs, task completion rate, escalation rate, quality and cost per completed task.
Then measure behavior quality: whether the agent chose the correct tool, how often it needed correction, whether it escalated ambiguous cases correctly and whether it attempted actions outside the intended scope.
The third layer is adoption. If employees do not trust the system and work around it, a technically successful agent has little business value.
Who builds AI agents?
AI agents are not only a programming task.
Someone who understands the business process must define what correct work looks like. Data and system owners need to approve access. Technical specialists need to design integrations, permissions and observability. A business owner needs to decide whether the pilot has produced enough evidence to continue.
The technical team builds and integrates the system, but the business defines what the agent is allowed to do and what counts as success.
So the question “who builds AI agents?” has two answers: specialists build the technical system, while the organization must define the process, boundaries, sources and accountability with them.
How to start with limited risk
Choose a task that is frequent, structured enough to test and has a visible manual cost.
Give the agent a limited tool set. A first version can be read-only and only recommend the next action. Additional actions can be introduced only after tests show sufficient quality.
Track failures and exceptions. Agents improve through better data, rules, tools, permissions and evaluations, not only through a better prompt.
The goal of the first phase is not maximum autonomy. It is evidence that the system can help reliably on a real task.
AI agents as part of a broader AI strategy
AI agents can become a powerful layer in a business system, but they do not replace organized processes, reliable data or accountability.
An organization that already knows where it loses time, has controlled sources and can define rules will find it easier to build a useful agent. An organization that skips those steps gets a more sophisticated version of its existing disorder.
Positive and Cybercompany therefore treat AI agents as part of a broader AI strategy: problem first, then workflow and data, followed by tools, access rights, human checkpoints and a measurable business outcome.
Explore the Cybercompany AI ecosystem, read AI strategy for companies or begin with the company assessment.
Frequently asked questions
What is an AI agent?
An AI agent is a system in which an AI model can use defined tools, data and rules to work through multiple steps toward a goal, with boundaries and human checkpoints where required.
What is the difference between an AI agent and a chatbot?
A chatbot is primarily a conversational interface that returns an answer. An agent can use tools and perform permitted actions across multiple steps, such as checking status, preparing a task and requesting approval.
Should an AI agent work completely autonomously?
Not necessarily. Autonomy should depend on risk. Low-risk actions may be automated, higher-impact actions can require human approval, and accountable legal, financial or strategic decisions should remain human.
How should a company start with AI agents?
Start with one frequent, measurable task, document the baseline, define the required sources and tools, restrict permissions, set human checkpoints and test the system against real and difficult scenarios.
Who builds AI agents?
The technical team builds and integrates the agent, but process owners, data owners and security stakeholders must define the rules, permissions, expected outcome and accountability together.